WEB SYSTEM UPGRADE × SECURITY REMEDIATION
Move your legacy web system
to a modern, secure stack.
We upgrade web systems still running on end-of-life PHP and framework versions to a modern, secure environment, one step at a time. Alongside the upgrade, Việt Vang scans the entire codebase for vulnerabilities with its own in-house diagnostic tool, then fixes every finding and re-scans to prove it.
Laravel
CodeIgniter
Other PHP frameworks
PHP runtime & servers
Case study (Laravel): 4 systems upgraded together
→
0
Vulnerabilities & defects found (before → after fixing)
01 / CHALLENGES
Does this sound familiar?
Running on unsupported versions
PHP 7 and older framework versions (e.g. Laravel 8) have reached end of life. New vulnerabilities no longer get patched.
Nobody knows what’s inside
The original developers are gone, and no one can say where the risks are or how serious they are.
Afraid an upgrade will break things
Worried that moving to a new version will break features that work today, so the upgrade keeps getting postponed.
Audits stop at the report
External security audits deliver a report, and fixing what they find means hiring someone else.
02 / OUR OWN TOOL
Việt Vang’s in-house diagnostic tool
“VV Laravel Checker”
A quality and security scanner built in-house by engineers with years of hands-on Laravel project experience. It goes deep into the Laravel-specific patterns that generic scanners tend to miss (route definitions, Gates / Policies, Blade templates, Eloquent) and tells you exactly where the problem is, why it’s dangerous, and how to fix it.
FEATURE 1
Custom OWASP-based rules
Detects broken access control, IDOR (acting on other users’ data), XSS, SSRF, open redirects, CSRF, misconfiguration, dangerous code and more, with rules tailored to Laravel.
v
FEATURE 2
Many checks in one run
Alongside the custom rules, it runs known-vulnerability checks on dependencies (composer audit), PHPUnit and static analysis (PHPStan / PHP_CodeSniffer) in a single pass.
FEATURE 3
Prioritized action plan
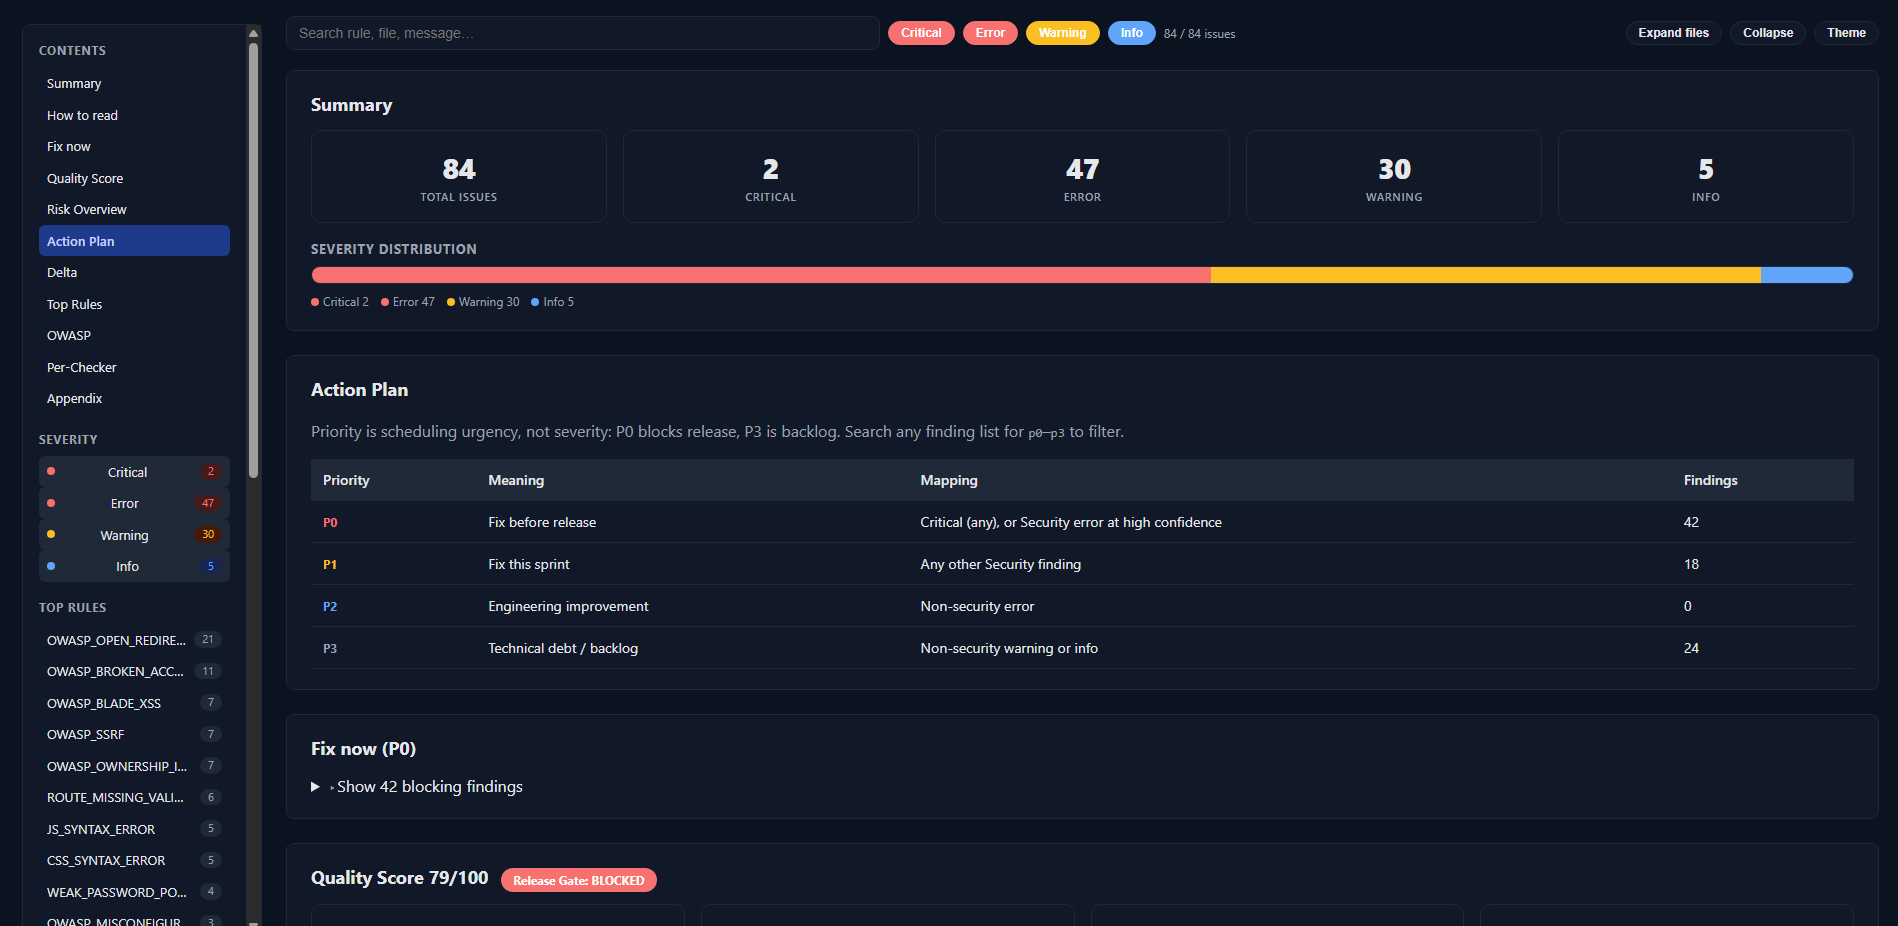
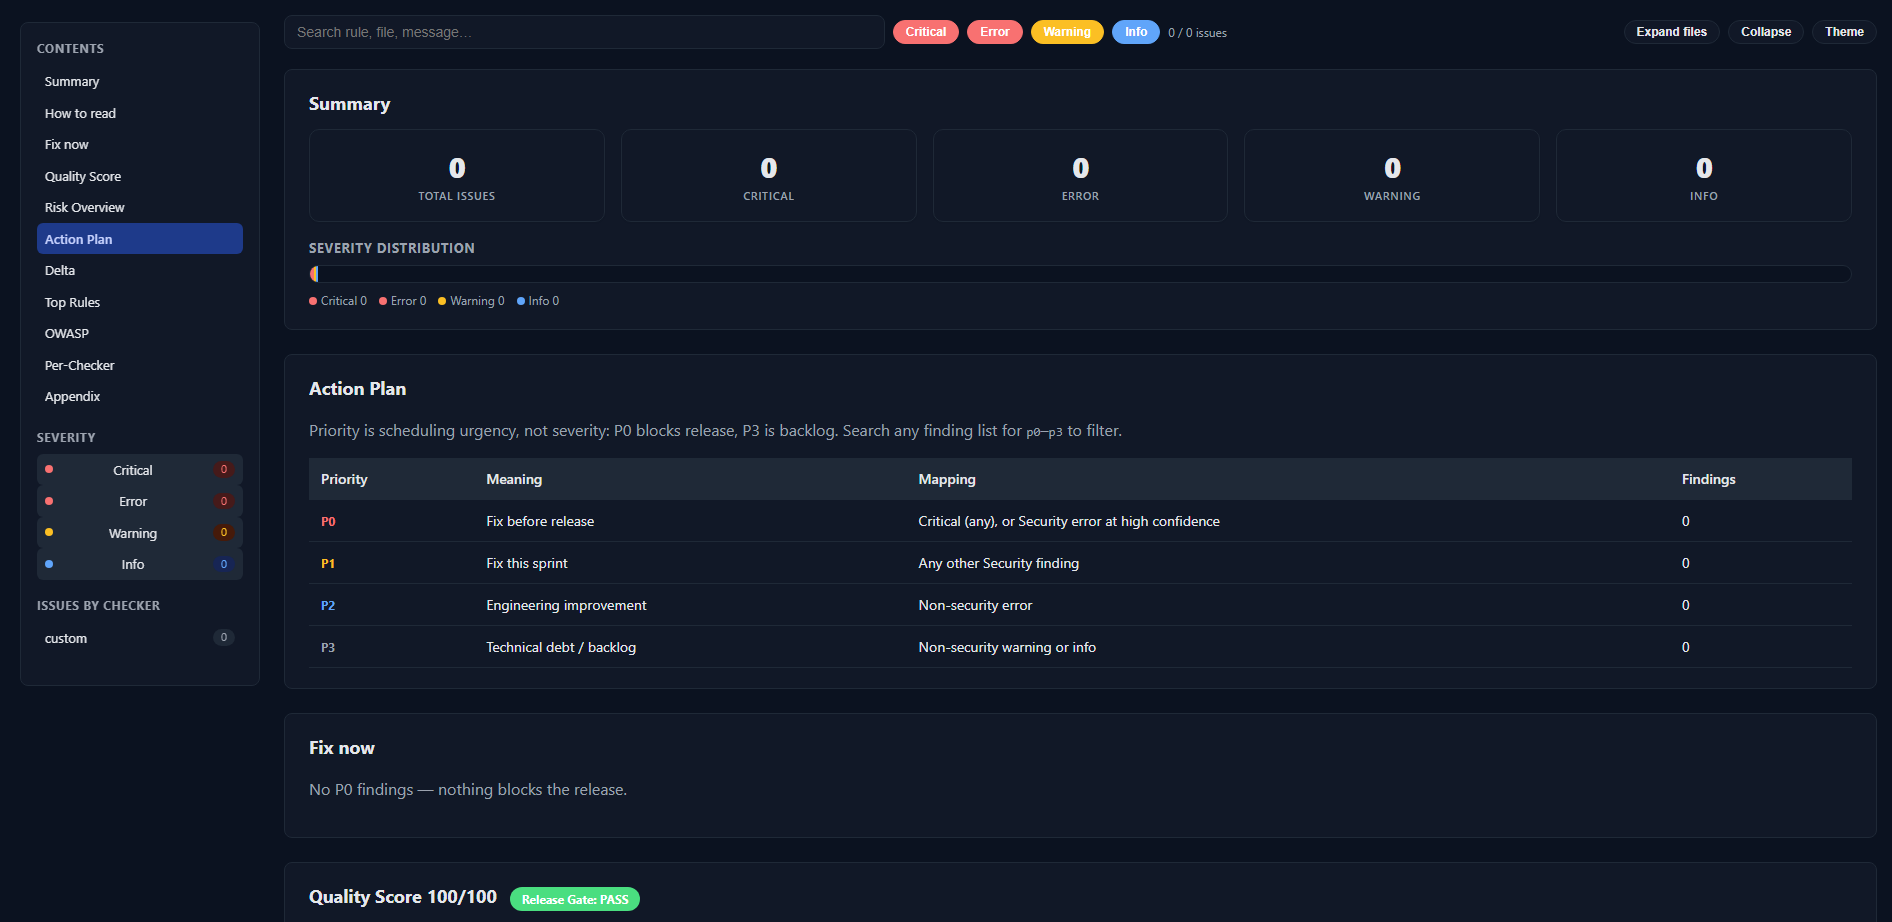
Findings are sorted by severity (Critical / Error / Warning / Info) and fix priority (P0–P3). A Quality Score and a Release Gate decision are calculated automatically.
FEATURE 4
Results proven in numbers
Before and after results are matched rule by rule and file by file, so the report shows exactly how many issues were fixed, how many remain, and how many are new.
Key detection rules
OWNERSHIP_IDOR
BLADE_XSS
SSRF
OPEN_REDIRECT
CSRF
SESSION_FIXATION
MISCONFIGURATION
WEAK_PASSWORD_POLICY
UNSAFE_EVAL
OBFUSCATED_PHP
ROUTE_MISSING_VALIDATION
A real diagnostic report
Every run produces an HTML report you can open in any browser (real screenshots, project names hidden).
Before: 84 findings ・ Score 79/100 ・ Release blocked
After: 0 findings ・ Score 100/100 ・ Ready to release
03 / CASE STUDY
Case study: a live business-matching platform (Laravel)
Without taking the service offline, we migrated four codebases step by step from Laravel 8 → 9 → 10 → 11 and PHP 7.x → 8.3. In parallel, we scanned and fixed them with VV Laravel Checker, then re-scanned under identical conditions to compare before and after.
PROJECT PROFILE
A business-matching web service
run by a Japanese company
A platform that connects companies and helps them do business together. It is live in production and used every day by companies around the world.
Findings by system
103
0
80
0
95
0
84
0
By severity (all 4 systems)
* A small number of findings were reviewed for impact and then deliberately excluded in the configuration file, with the reason recorded. Excluded items remain traceable in the report.
04 / FIX EXAMPLES
We find it, and we fix it
We don’t stop at the diagnosis: our engineers fix every finding themselves. Below are fixes from the real project (code simplified for illustration).
Other companies’ data could be deleted
Changing an ID was enough to delete another supplier’s price list. We added an ownership check.
- $item = PriceList::find($request->id);
- $item->delete();
+ $this->authorize('ownsSupplierResource', [PriceList::class, $id]);
+ $item = PriceList::query()
+     ->where('id', $request->id)
+     ->where('supplier_id', Auth::user()->supplier->id)
+     ->first();
+ $item?->delete();
Screens and APIs open without login
Critical routes such as data imports had no authentication. We added authentication and permission checks.
- Route::get('/import_supplier',
-     [ImporterController::class, 'importSupplier']);
+ Route::get('/import_supplier',
+     [ImporterController::class, 'importSupplier'])
+     ->middleware('auth');
+ // In the controller: $this->authorize('runLegacyImport');
Script injection on screen (XSS)
Admin templates printed data without escaping. We switched them all to safe output.
- <a href="{!! url('detail/' . $item->id) !!}">Details</a>
+ <a href="{{ url('detail/' . $item->id) }}">Details</a>
Unsafe redirects
Redirects built from raw URL strings now go through one shared class that validates against an allow-list.
- return redirect('/404');
- return redirect('/detail-company.html/' . $id);
+ return SafeRedirect::toNotFound();
+ return SafeRedirect::toRoute('buyer.detail', ['id' => $id]);
We also removed wildcard CORS settings, strengthened the password policy, took /phpinfo offline, and removed an old library containing dangerous eval calls (about 2,300 lines), among other fixes.
05 / SERVICE SCOPE
One team, from assessment to post-release monitoring
Assessment & quick fixes
Before the full upgrade, we apply measures that work immediately: hardening php.ini (hiding version info, strict session mode, etc.), right-sizing resource limits, and rate-limiting login and upload.
Upgrade to PHP 8.3, 8.4
We rebuild the container images and swap them in while keeping data and volumes intact, then verify the version and run smoke tests.
Step-by-step framework upgrade
Laravel, CodeIgniter and others: we move one version at a time, following each framework’s official upgrade guide (e.g. Laravel 8 → 9 → 10 → 11). Dependencies are updated and breaking changes in mail, file storage and configuration are fixed.
Security diagnosis & remediation
We scan the code before fixing with our own tool (VV Laravel Checker for Laravel projects) and fix every finding. A re-scan then confirms zero remaining and zero new issues, and you receive the report.
Credentials & permissions
We secure database credentials and .env files, correct file permissions (removing wide-open 777 permissions, etc.) and review connection settings.
Regression testing, release & monitoring
Regression tests cover the core features: login, CSV import, email, uploads, exports and more. We deploy to production within a maintenance window (with a 15-minute rollback plan) and monitor logs for 1–2 weeks after release.
06 / SCHEDULE
Standard schedule: 10 working days
Team: 2 developers + 1 tester (example from a 2-app Laravel project; varies by framework and size)
07 / PRICING
Indicative pricing
Example: a 2-app system (PHP upgrade + Laravel 8 → 11)
US$2,500
About 15 man-days ・ US$170 per man-day
* Indicative price based on a real project quotation. Actual cost depends on the framework, codebase size, versions and infrastructure. We also offer security diagnosis on its own, or can help you scope the fixes. The first consultation and a rough estimate are free.
08 / WHY VIỆT VANG
Why Việt Vang
Objective quality, measured by our own tool
No guesswork. Before and after are scanned against the same standard, and you get the results as numbers and a report.
Security track record with Japanese clients
We have carried out website information-security assessments for Japanese state-owned companies and built systems for clients in Japan and Germany.
Diagnosis to fixes to operations, in one place
We don’t stop at the report. The same team takes responsibility for fixes, testing, production release and monitoring.
Start with a free consultation
Tell us which PHP version and framework your system runs on, and roughly how large the codebase is. We’ll propose the scope, timeline and estimated cost.
7-9-11 Tran Xuan Hoa Street, Ho Chi Minh City, Vietnam